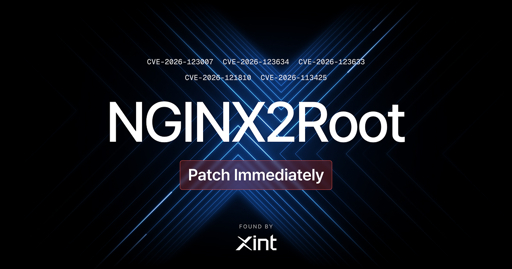
WHY do all new vulnerabilities have to use this inane naming scheme? These are grown-up problems. Can we use grown-up names?
If someone finds another vulnerability in Nginx that gives root access, will it be called NGINX3root or NGINX2root2?
(Yes, I know this is a petty complaint)
You’re right, at the least the name should have the year in it so that we know if it’s a new vulnerability or an old one.
And since a product can have multiple vulnerabilities in the same year we should have a number that increments with each new vulnerability found.
Also, since one vulnerability can affect multiple products (eg. a vulnerability in a library), we can’t use the product names to identify the vulnerability (as that could be quite a long list). We will just use the acronym for our naming scheme so that we can distinguish our list of numbers from other lists of numbers like book ISBNs or ICQ numbers.
We could call our naming scheme the Cool Vulnerability Eponym.
So the vulnerability name would end up as something like
CVE-2026-123456.Lol, nice backronym! CVEs are great! They’re not very scannable in headlines, though. For that I would actually prefer product name to be involved. Just maybe not written as a Fast and Furious movie title.
Nginxroot3: Tokyo drift
2nginx2root2you
This is a much more descriptive name than SPECTRE or MELTDOWN though. I’ll take this scheme any day of the week.
2NGINX2root, followed by NGINX root: Tokyo Drift.
Just fyi, the nginx vulnerabilities are all impractical to use. The bugs are use after free, which will almost definitely lead to a crash in the worker process and have them be restarted.
That itself would make it about as bad as the mp-tcp style expoits lately, but it’s even weaker. If you could keep trying, you could strap an llm into figuring out a specific machine and after tons of compute eventually get out data or take controll of the nginx-owned process.
But, the restarts should restart that process, so I don’t see almost any risk unless you have address randomization disabled, which would be highly unusual.Unless I am missing something here, I see a bigger risk with an unmentioned loop that was also fixed in nginx. That one lets you make a worker thread hang, so you can disable a server until someone notices and restarts nginx. That ddos affects servers with tls1.3 support.
Also their “2root” is just a completely unrelated kernel bug they bundled for marketing, which is pissing me off tbh. All of this “security research” for marketing is the worst possible contradictory incentive. You wanna release as poorly as possible to maximize fear mongering.
They didn’t even release the bug, for all we know is as convoluted to use as the mp-tcp stuff and affects basically noone. Not that the nginx side is exploitable.Thank god I’m running IIS 5.
I will get into your network and send you netsend messages!
I’m running IIS 5.
But why?
The S stands for Secure.
Internet Ixplorer Secure
I am root. 🪵
Ruh roh rooby!