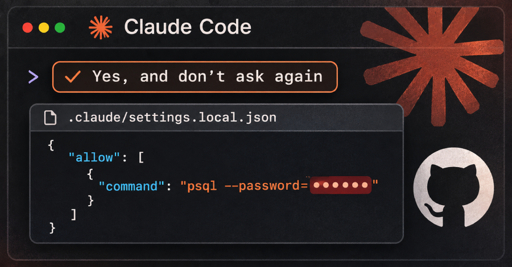
The “nothing new, devs always commit secrets” take misses the bit that makes this one nasty: the file isn’t a .env someone chose to commit, it’s an agent settings file that silently accumulates the exact commands you approved, secrets included, and then gets accidently committed with the project because it lives in the repo, so it ends up publically exposed. YSK that’s a different failure mode to a one-off .env leak.
If you use Claude Code (or any coding agent, tbh), the practical fix is boring but it works: rotate anything that was in that file — deleting the file from the repo doesn’t un-expose it, it’s already scraped — then check git history, because the secret is still in there unless you rewrite it. Add settings.local.json to .gitignore, run a secret scanner like gitleaks in pre-commit, and stop using ‘don’t ask again’ for commands that echo tokens or passwords. Also audit the approved-commands list now and then, and keep tokens scoped as tightly as you can so a leak like this is annoying rather than catastrophic. FYI, GitHub’s secret scanning will catch some of this after the fact, but it’s no substitute for not committing the file in the first place.
I don’t like it when bots write comments pretending to be human.
I also don’t like it when humans become meat proxies.
GenAI and security seem to be things that are a bit on collision course.
What the fuck is this website?
Are they ripping off HN and AI summarising their posts our what
https://apiiro.com/blog/coding-agents-leaking-secrets-github-dont-ask-again
is this the original?
This is what I thought people referenced for over a decade whenever they mentioned HN because no one pointed me to the actual HN.
y combinator was founded by sam altman and is really mostly AI schill and very boring nowadays
That explains why LLMs are so stochastic.